
EtherInsights film
Microsoft 365 security assessment: Zero Trust, read-only
Run over a hundred Zero Trust checks and compare tenant settings with security baselines, read-only. See findings by risk, investigate changes, share a report.
Notes
- The check count is the recorded run's own and varies by tenant and licence.
- The checks cover four pillars: identity, devices, network and data.
- The 29 DISA STIG rules are 14 Entra per-setting checks and 15 checks that an Intune baseline is present.
- The DISA STIG comparison is not a full STIG compliance assessment.
- The assessment reports findings and recommended actions; it does not change the configuration.
Chapters
- 0:00Your Secure Score says 77%, but which checks fail?
- 0:12More than a hundred Zero Trust checks
- 0:28Findings, highest risk first, with evidence
- 0:42Who changed what, and a report to work from
- 0:52Read-only, so you review the evidence first
Transcript
- 0:02Your Secure Score says 77%.
- 0:05Then your auditor asks which Zero Trust checks fail, and who changed what.
- 0:12More than a hundred checks give your security review a more detailed starting point.
- 0:19EtherInsights runs Zero Trust checks based on Microsoft's assessment and compares your tenant settings with security baselines.
- 0:28See the findings, highest risk first: forty to clear, seven of them high risk.
- 0:36Open any setting for the evidence and the guidance.
- 0:42Investigate changes: what moved, who moved it, and when.
- 0:48Give your team a report to work from.
- 0:52The assessment is read-only, so you can review the evidence before deciding what to change.
- 0:59Try EtherInsights free for fourteen days on your own tenant.
More films
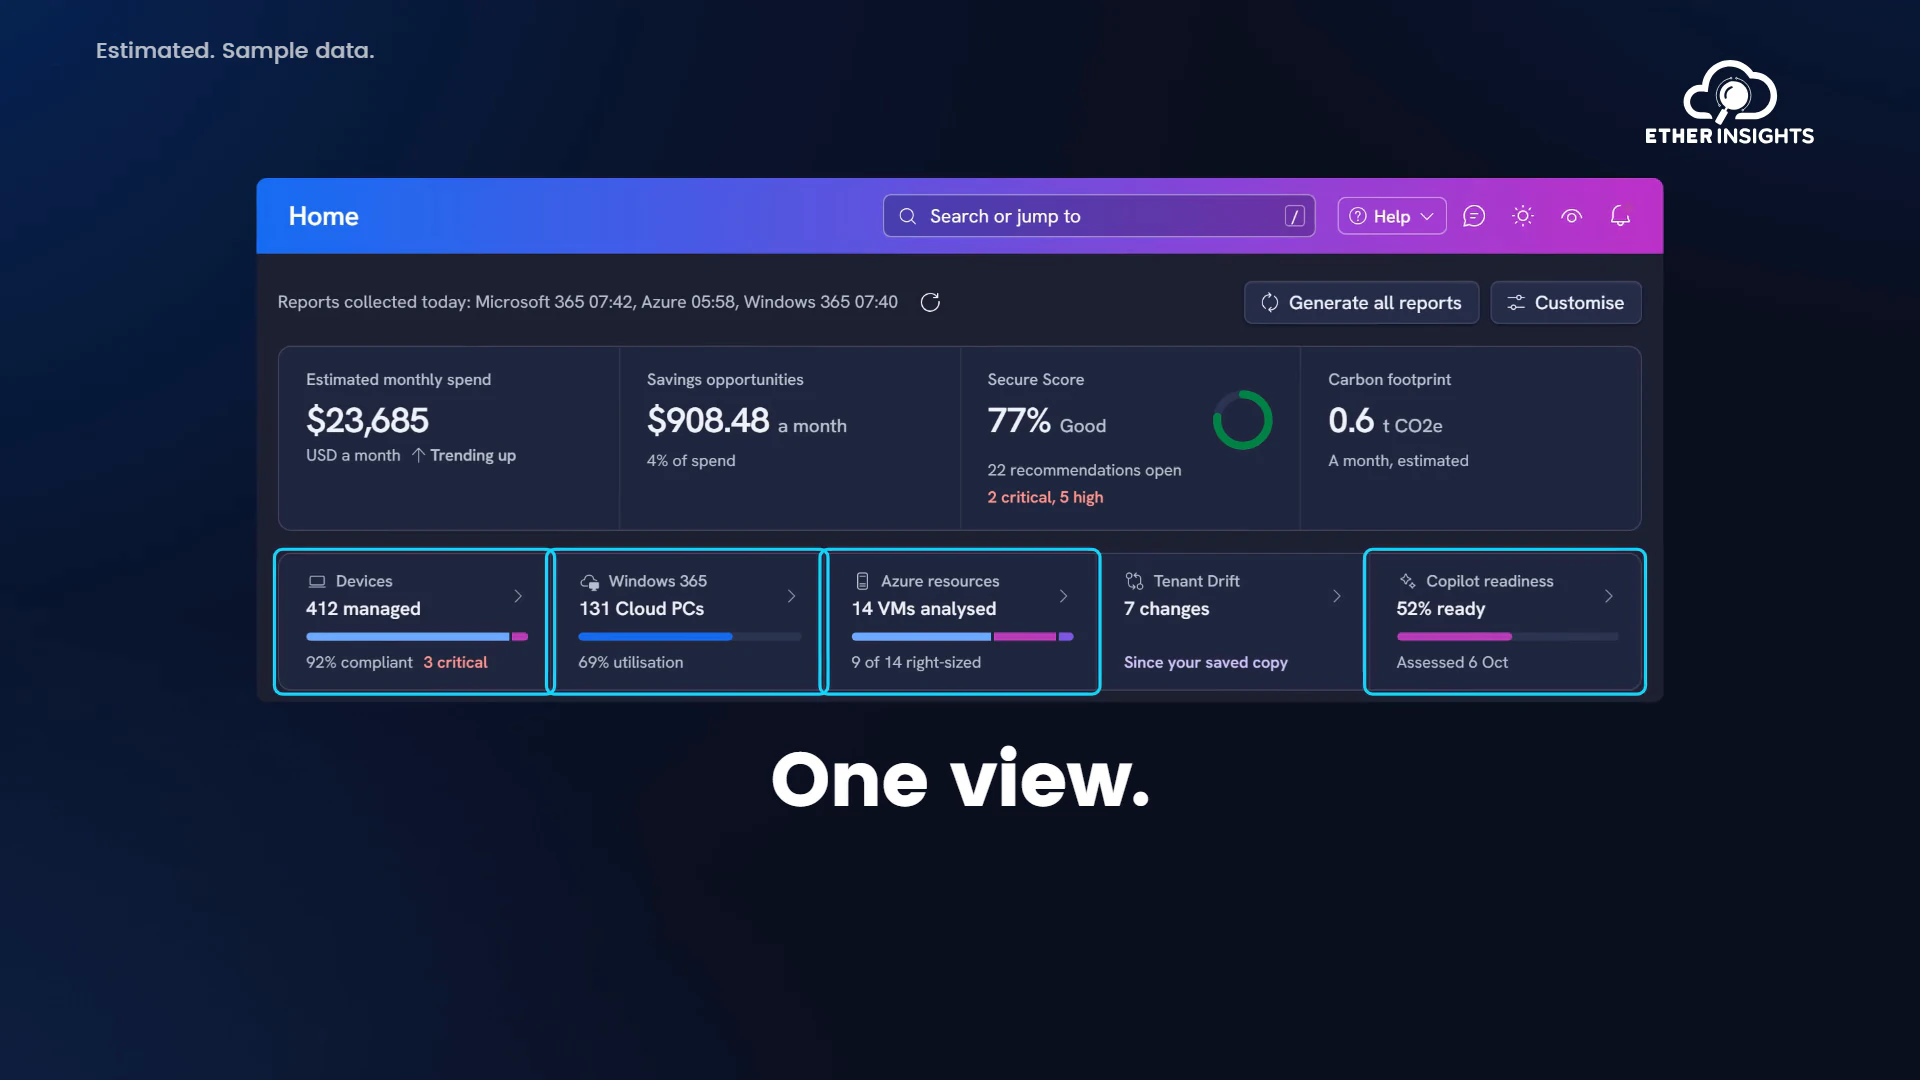
EtherInsights film
EtherInsights overview: Microsoft 365 and Azure in one view
Running time 1:20
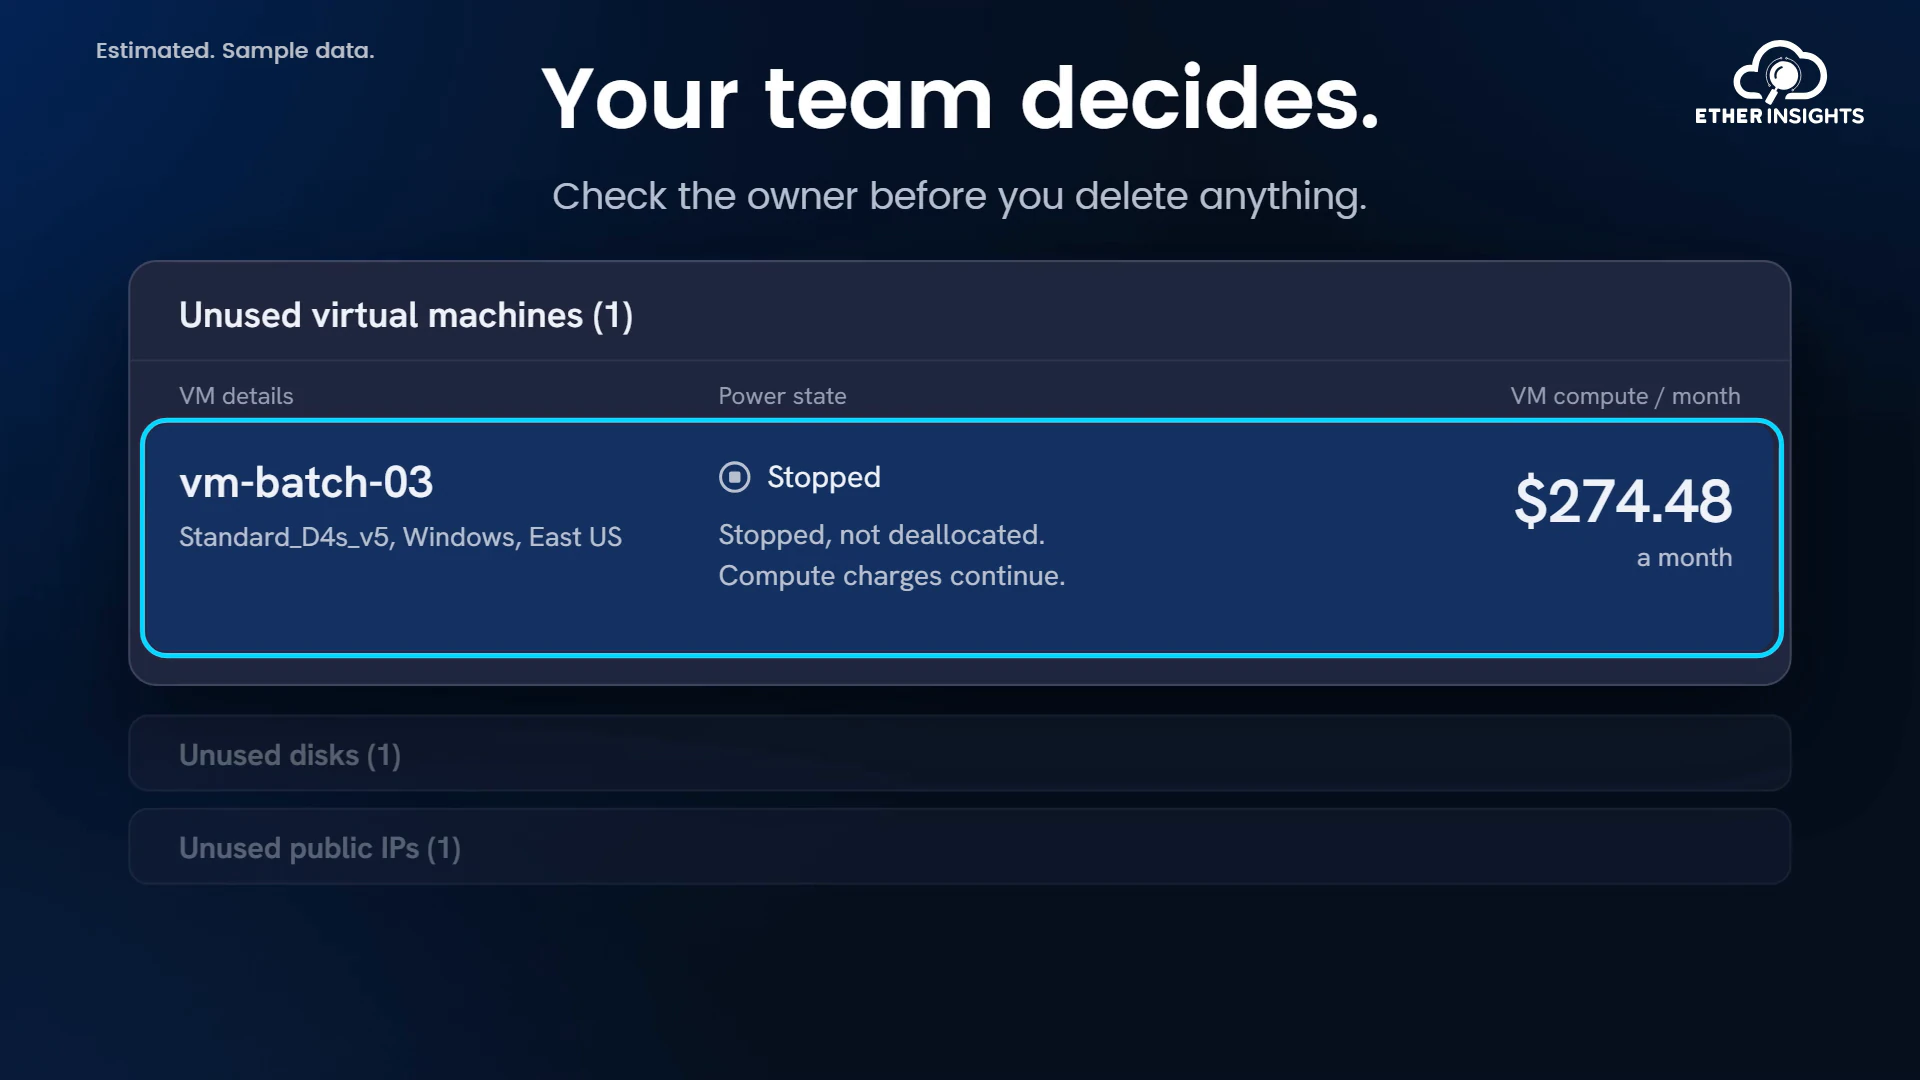
EtherInsights film
Find idle Azure resources and what they cost each month
Running time 1:10
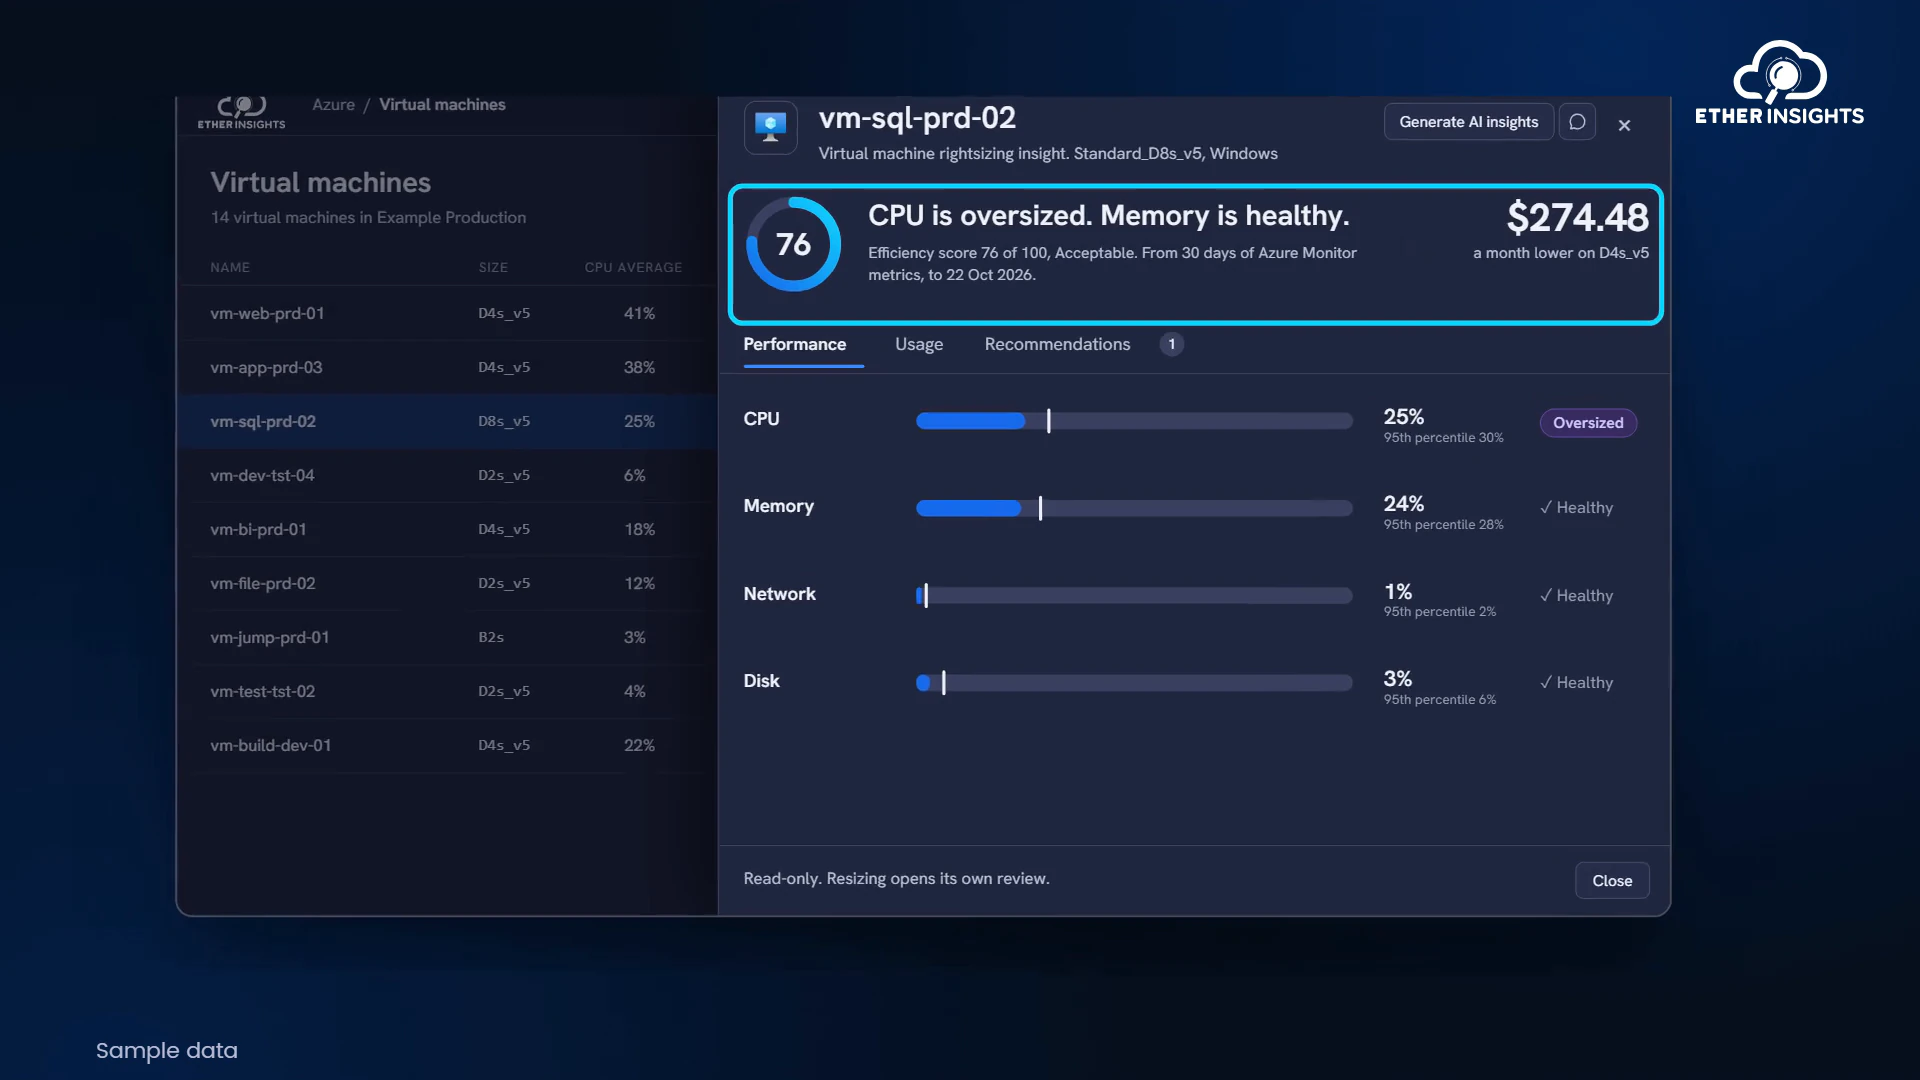
EtherInsights film
Azure VM right-sizing with usage and cost evidence
Running time 1:05